Talks
Talks I have given, plus ones that are coming up. Recordings play right here, with no YouTube and no third parties.
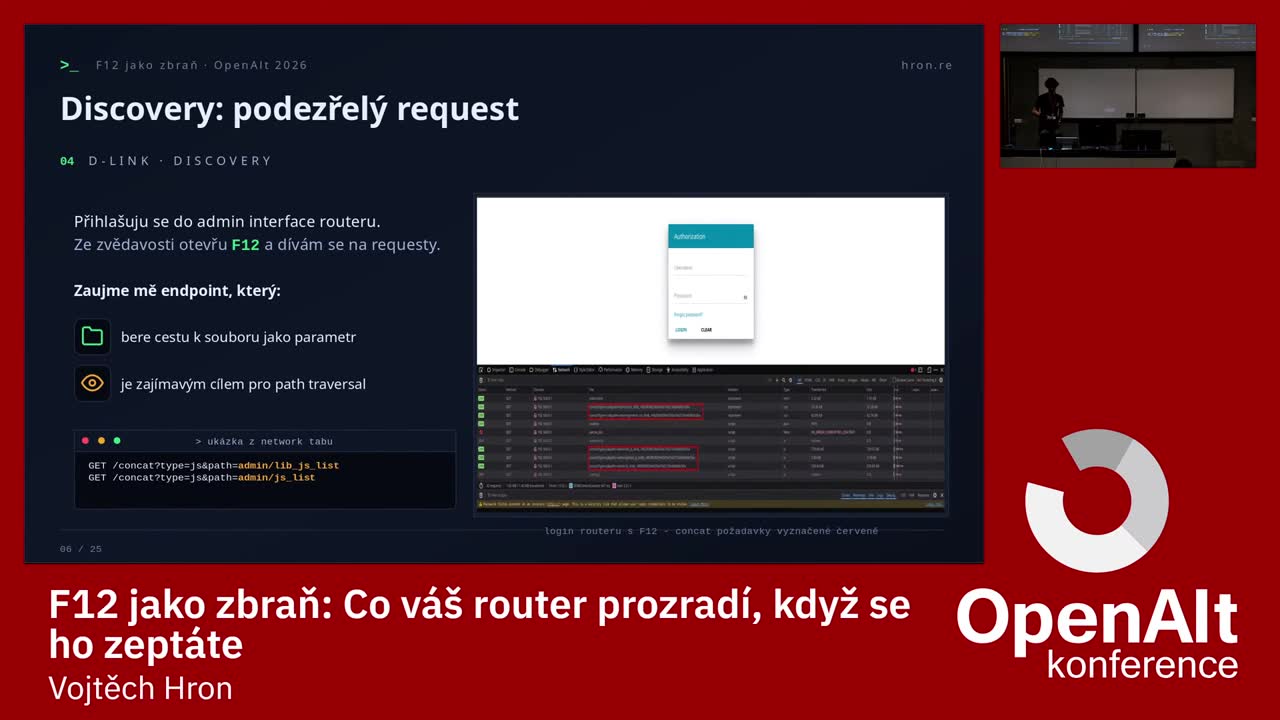
F12 as a Weapon: What Your Router Reveals When You Ask It
How often do you open F12 when logging into your router? I did it twice and found a security bug both times. I’ll show two vulnerabilities in home ISP routers. On one, from O2, the router hands the admin password to anyone. We’ll go from a suspicious request through reverse engineering in Ghidra to a live exploit. You don’t need to know crypto or reversing, just curiosity and F12.
Play the talk
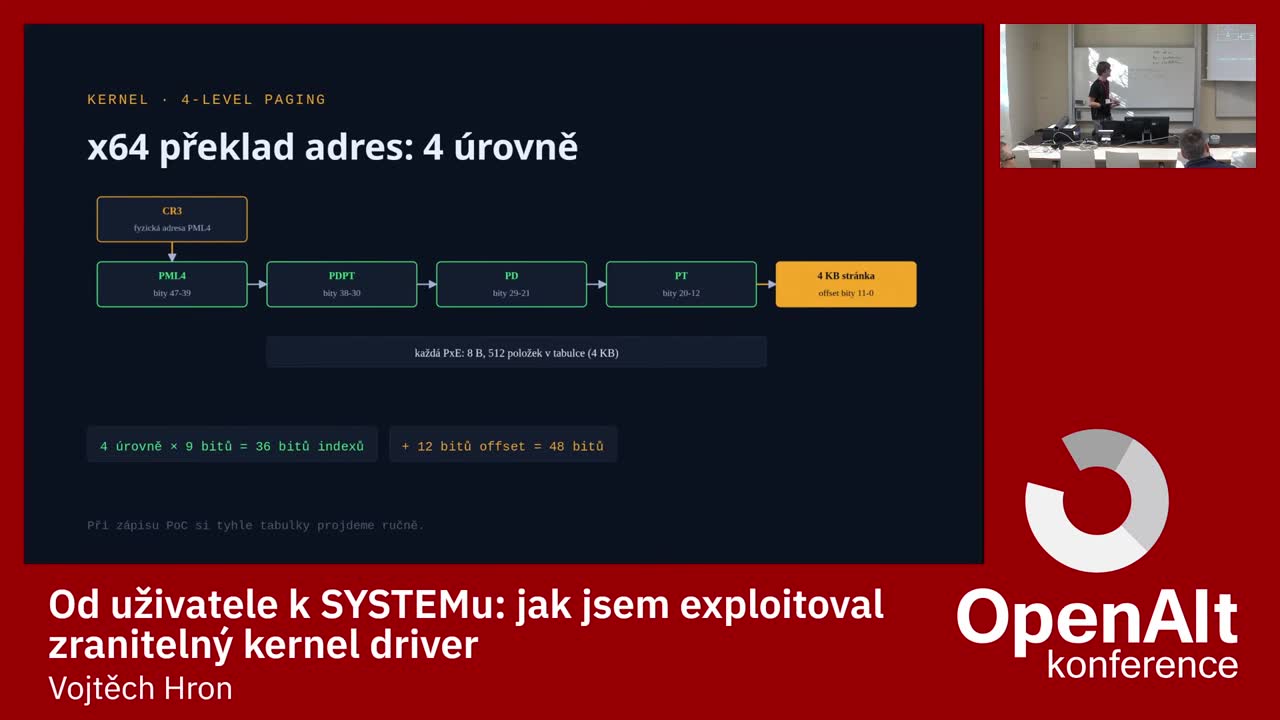
From User to SYSTEM: How I Exploited a Vulnerable Kernel Driver
How I wrote a privilege escalation exploit from scratch for a real signed Windows driver, ktapi.sys. From kernel foundations - protection rings, virtual and physical memory, page tables, through reverse engineering in Ghidra and stealing the SYSTEM token to a working PoC. I close with the defenses that actually work against this class of attack, abused by ransomware too: HVCI, WDAC, LOLDrivers.
Play the talk